Open source · Rust · Apache-2.0

The ultimate
DNS server.

One binary that answers your zones, forwards the rest over encrypted transports, signs and validates DNSSEC, filters what you don't want and shows you every query.

curl -fsSL https://dnsy.dev/install.sh | sh
Windows: irm https://dnsy.dev/install.ps1 | iex · install options, archives and building from source
Feature matrix

Everything a DNS server
should do. In one binary.

The whole DNS layer, DNSSEC included, is written in this repository. No DNS library underneath; only ring for raw cryptography.

  • Protocols

    • UDP and TCP
    • EDNS0, EDE, padding
    • TCP pipelining
  • Encrypted

    • DoT with mTLS
    • DoH with tokens
    • HTTP/2, GET and POST
  • DNSSEC

    • Validating forwarder
    • Zone signing, NSEC3
    • Rollover, DS export
  • Load balancing

    • Upstream groups
    • Weighted, latency, failover
    • Health checks
  • Cache

    • Negative caching
    • Serve-stale, prefetch
    • DNSSEC-aware entries
  • Filtering

    • Hosts, domain, adblock lists
    • Allowlist, ACL, rate limits
    • Response-IP policy
  • Zones

    • JSON zone files
    • Hot reload
    • BIND export, signed
  • Observability

    • Query log, live tail
    • Stats and rollups
    • Dashboard
  • Panel and API

    • Web panel, roles
    • REST + OpenAPI 3.1
    • Scoped API tokens
  • One binary

    • Embedded SQLite
    • One TOML config
    • Linux, macOS, Windows
01 · The pipeline

Every query takes
the same path.

Whatever the transport, each request runs through one pipeline. The first step that can answer ends it, and every request emits exactly one query event for the log and the stats.

Guard
ACL, per-client rate limit, sanity checks, no zone transfers
Decide
Blocklists, then your own zones, authoritative
Resolve
Cache, then upstream groups with a hard deadline; identical misses share one exchange
Trust
DNSSEC validation, scrubbing, response-IP policy
Shape
The client's id and flags back, AD and EDE added
CLIENTS UDP :53 TCP :53 DoT :853 DoH :443 PIPELINE ↳ blocked: block_mode answer + EDE ↳ local: AA, never cached ACL limit sanity filter zones RD cache miss upstreams ×3 hit validate scrub resp-IP shape ANSWER AD · secure one QueryEvent per request → query log, stats
02 · DNSSEC

Signs your zones.
Checks everyone else's.

DNSY validates the chain of trust from the root down for forwarded answers, and signs your own zones with keys it generates, stores encrypted and rolls over.

Validation
strict, permissive or off; negative trust anchors
Signing
ECDSA P-256 or Ed25519, NSEC or NSEC3
Lifecycle
automatic re-signing, KSK and ZSK rollover
Registrar
DS records ready to paste
CHAIN OF TRUST . (root)DNSKEY KSK 20326 · trust anchorRRSIG ✓ com.DS signed by the rootDNSKEY · RRSIG ✓ example.com.DS signed by com.A 93.184.216.34 · secure YOUR ZONE, SIGNED (EXAMPLE) example.org. KSK Ed25519 active ZSK Ed25519 active ZSK Ed25519 pre-published denial NSEC3, opt-out re-sign before expiry rollover ZSK pre-publish DS for your registrar example.org. IN DS 4821 15 2 9F86D081884C7D659A2FEAA0…
03 · Private by default

Encrypted transports,
locked down.

Serve DNS over TLS and DNS over HTTPS next to plain DNS. Require client certificates on DoT, hand out scoped tokens for DoH, and forward upstream over TLS too.

DoT
mTLS off, optional or required, with an allowlist
DoH
token in a header or the path, HTTP/2
Upstream
forward over UDP, TCP or TLS
laptopclient cert ✓ browserbearer token routerplain, LAN only DoT :853DoH :443 UDP :53 DNSYACL · mTLS · tokens TLS 1.1.1.1 :853 9.9.9.9 :853 10.0.0.1 :53
04 · Web panel

See every query.
Change anything.

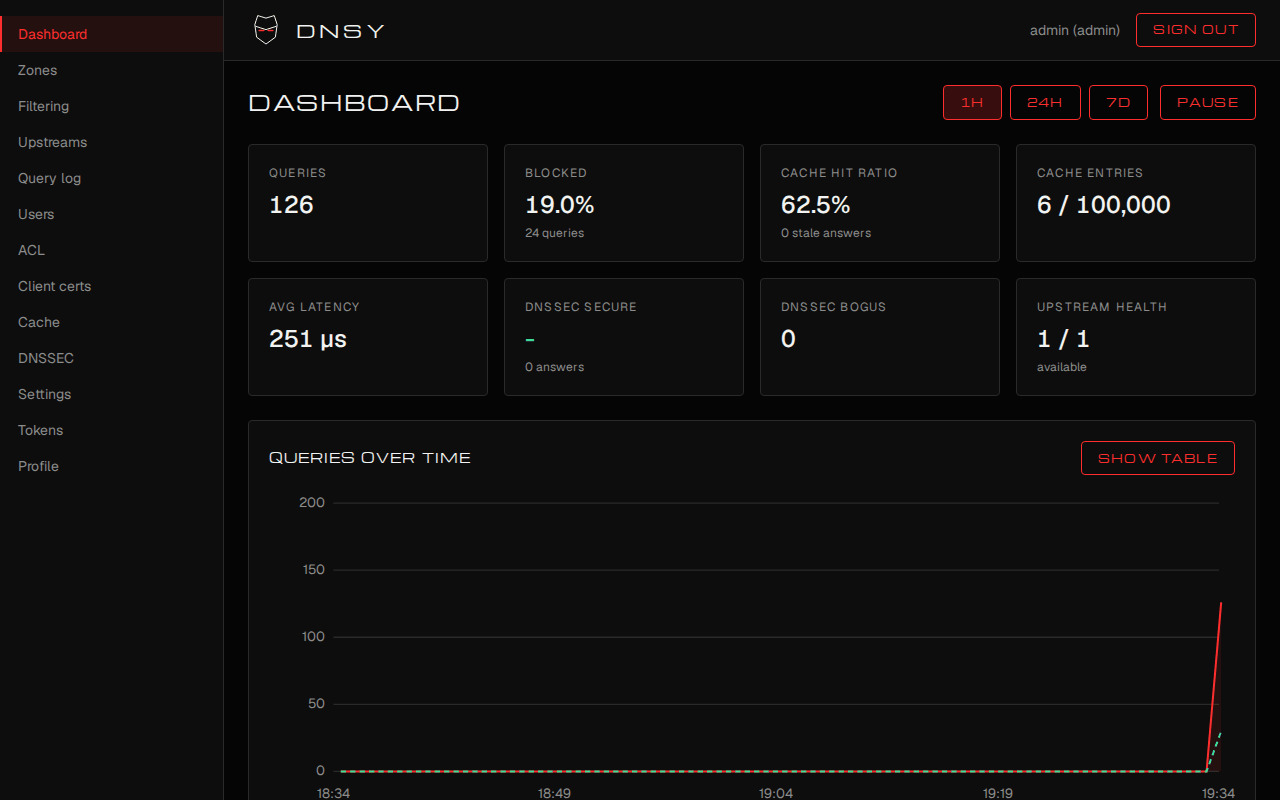
A web panel built into the binary: dashboard, query log with live tail, zone editor with a DNSSEC tab, filtering, upstreams, users and tokens. Everything it does is also in the REST API.

Dashboard
queries, latency, cache hit ratio, blocked, DNSSEC outcomes
Query log
search, filter and tail live
REST API
OpenAPI 3.1, scoped tokens
The DNSY dashboard: query, blocked, cache and DNSSEC tiles above a queries-over-time chart.
Get started

Run it in a minute.

curl -fsSL https://dnsy.dev/install.sh | sh